
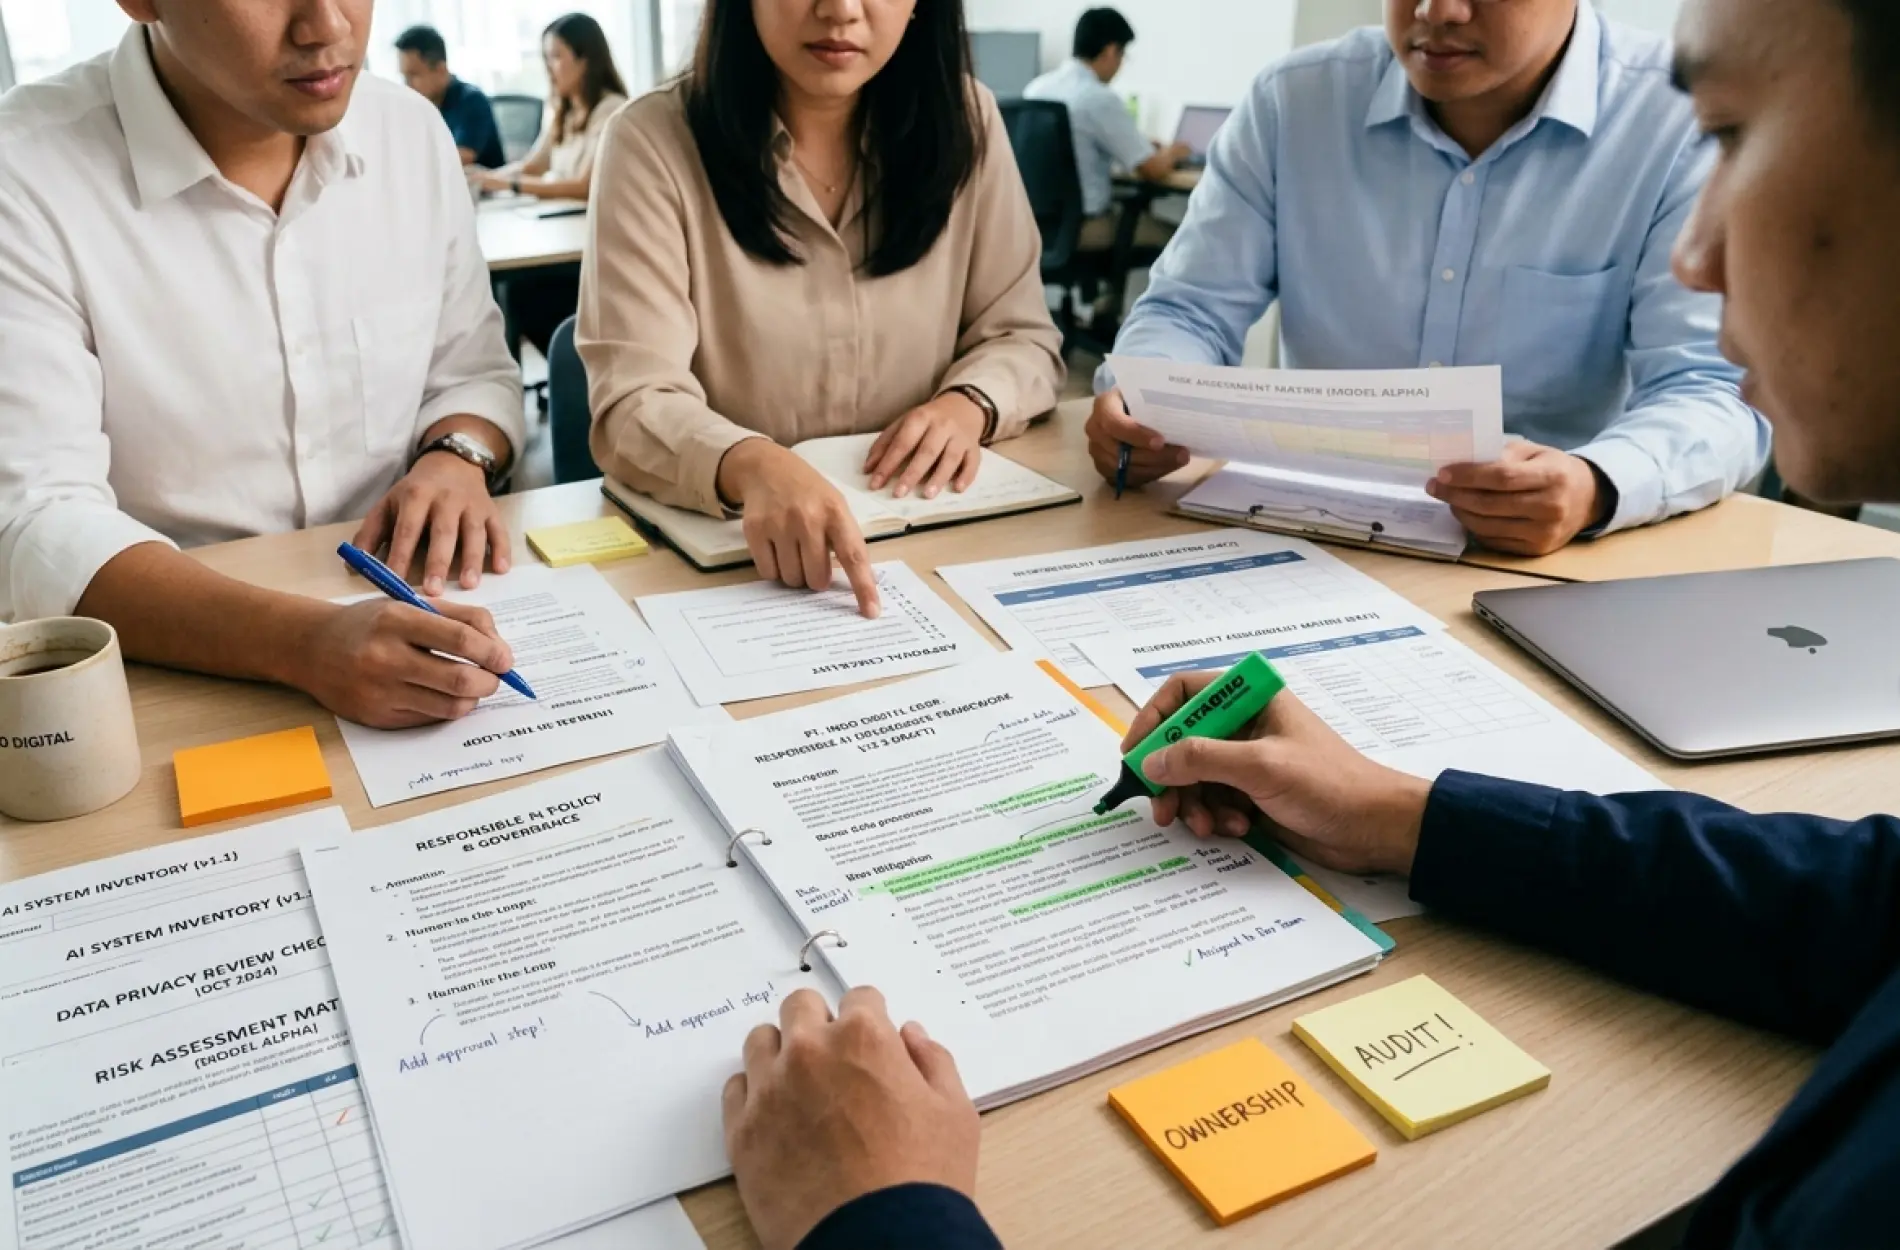
The wider AI (Artificial Intelligence) use spreads across an organisation, the more a clear responsible AI policy matters.
Without a structured framework, each team applies its own standard. That opens the door to risks around data security, accuracy, bias, transparency, and accountability when a system produces a decision that turns out to be wrong.
A responsible AI policy needs to cover more than principles alone. Organisations also need to establish who holds accountability, how risk gets assessed, which actions are permitted, and how systems are monitored once they go live.
The five steps below provide a practical foundation.
Why a Formal Policy Matters
Some organisations assume a written policy can wait while AI use remains limited. That assumption carries risk, since AI adoption typically moves considerably faster than anyone anticipates.
AI systems tend to arrive through channels nobody is watching. The marketing team subscribes to an AI-powered analytics tool, customer service deploys a chatbot, and operations picks up an automation platform. Each runs to its own standard.
The absence of a policy produces several consequences. Accountability blurs when a system makes a decision that harms a customer. Organisations also struggle to answer regulator questions about how their AI systems are supervised. Risk accumulates quietly, then surfaces at the least convenient moment.
A responsible AI policy addresses this by setting standards that apply across the organisation, so every decision has a clear reference point.
Step 1: Take Stock of Every AI System
Policy development cannot start without understanding what actually needs governing.
Map every system in operation. Compile a list of AI systems in use across all departments, covering internally developed tools, third-party purchases, and AI capability embedded within software already in place.
Identify impact levels. Group each system according to its effect on customers and employees. Systems influencing financial decisions, service access, or individual assessments warrant the tightest oversight.
Record the data involved. Document what each system processes, paying particular attention to anything handling personal information or other sensitive data.
Assign initial ownership. Identify who currently manages each system, even before a formal structure exists.
This inventory forms the foundation for everything that follows, since a policy drafted without knowing the actual scope risks being irrelevant from the outset.
Step 2: Define Principles That Are Specific
Principles establish the values behind a policy, but their usefulness depends entirely on how concretely they are written.
Avoid statements that are too general. A commitment to fairness offers no operational guidance on its own. A stronger formulation explains what fairness means in your specific context and how you would measure it.
Write principles that can be tested. Each principle should carry an indicator that allows verification. Transparency, for instance, translates into an obligation to disclose AI involvement in every customer interaction.
Reflect your industry context. Financial institutions face different demands from retail businesses. Your principles need to mirror the regulations and specific risks your sector actually carries.
Set priorities for when principles conflict. Certain situations put principles at odds, such as deep personalisation against privacy protection. The policy needs to state which takes precedence.
Step 3: Build the Governance Structure
A policy without a structure to enforce it remains a document with no practical effect.
Appoint senior accountability. Designate one person at leadership level who holds overall responsibility for AI governance across the organisation.
Form a cross-functional committee. Bring in representatives from technology, legal, compliance, information security, operations, and customer experience. Varied perspectives keep the policy from becoming either too technical or too abstract.
Define decision rights clearly. Set out who approves new AI deployments, who can suspend a system that is causing problems, and how escalation works in practice.
Establish a review cadence. Determine how often the committee meets and what the standing agenda covers, including evaluation of live systems and assessment of proposed deployments.
Need support developing AI governance across your organisation? Get in touch with the KPSG team to discuss responsible AI implementation through our CXaaS solutions. Consultation is free of charge. [Schedule a Free Consultation.]
Step 4: Write the Operating Procedures
Principles need translating into concrete steps teams can follow day to day.
Pre-deployment assessment procedure. Build a checklist that must be completed before any new AI system goes live, covering risk assessment, data quality review, and regulatory compliance verification.
Customer disclosure procedure. Set the standard for how and when AI involvement is disclosed, including sample wording teams can use across different channels.
Faulty decision handling procedure. Spell out what happens when a system produces an incorrect decision, covering correction mechanisms, communication with affected customers, and internal reporting.
Bias testing procedure. Define the method and frequency of testing to confirm systems are not producing outcomes that disadvantage particular groups.
Logging procedure. Require records of every significant decision an AI system makes, including the data behind it, for audit and investigation purposes.
Step 5: Establish Continuous Monitoring
A policy written once and then left alone loses relevance as technology and regulation move on.
Set monitoring indicators. Determine metrics that reflect policy compliance, covering system accuracy, escalation frequency to human agents, and complaints relating to automated decisions.
Run periodic audits. Schedule a comprehensive review of all AI systems at least annually, more frequently for high-impact ones.
Update the policy as things change. AI regulation continues to develop, as does the technology itself. Regular review keeps the policy aligned with current conditions.
Gather feedback from the ground. Teams applying the policy daily often spot gaps that were invisible at the drafting stage. Their input is genuinely valuable for refinement.
Run regular training. A policy only works when everyone involved understands it. Recurring training maintains that understanding despite staff turnover.
Common Mistakes in Policy Development
The following errors frequently prevent a policy from working as intended.
Drafting in isolation from operational teams. A policy written solely by legal or technology risks being impractical once it meets daily operations.
Copying another organisation's framework wholesale. Every organisation carries a different risk profile, so a framework that works elsewhere may not translate.
Making the policy too rigid. Rules with no room for judgement tend to push teams towards workarounds outside official procedure.
Overlooking third-party AI systems. Vendor-supplied systems remain the responsibility of the organisation using them, so they belong within the policy's scope.
Failing to resource implementation. Policies require time and effort to run. Without allocated resources, implementation stalls at the document stage.
Conclusion
Building a responsible AI policy calls for a systematic approach, starting with an inventory of systems in operation, moving through specific principles, a governance structure, and operating procedures, and ending with continuous monitoring.
Effective policies share recognisable traits. They are specific, testable, developed across functions, and backed by adequate resources to run them. A document that stops at value statements without operational guidance offers no real protection to either the organisation or its customers.
KPSG brings more than 35 years of experience in contact centre operations and customer experience management. We apply responsible AI principles across our CXaaS solutions, helping organisations ensure every technology deployment carries governance robust enough for innovation and accountability to move together.
Ready to make your business operations more efficient, scalable, and equipped to meet ever-evolving customer needs? Contact us here.Discover more professional insights and the latest industry trends here.
FAQ (Frequently Asked Questions)
What should a responsible AI policy contain?
A responsible AI policy typically sets out the organisation's guiding principles, its governance structure and associated decision rights, operating procedures for various situations, and mechanisms for monitoring and periodic audit.
Who should be involved in drafting it?
Drafting should involve a cross-functional group spanning technology, legal, compliance, information security, operations, and customer experience, so the policy ends up both practical and comprehensive.
Do smaller organisations need
Yes, though the scope can be simpler. Any organisation running AI systems that affect customers carries the same responsibility, regardless of its size.
How often should the policy be reviewed?
A comprehensive review at least annually is advisable, and sooner following regulatory changes, the deployment of a new high-impact system, or an incident warranting evaluation.
Do vendor AI systems need to be covered?
They do. Responsibility for a system's impact stays with the organisation using it, so third-party systems must meet the same standards as those developed internally.